// Contents
An engineer at the crypto exchange Binance searched the web for a popular AI coding assistant and, to install it, downloaded a tampered copy of Homebrew, a program Mac users rely on to install other programs. That was in June 2026. Binance’s security team spotted it, replaced his computer and rotated his passwords. Problem solved, or so it seemed. Four months later, on October 20, attackers got into the same engineer’s machine again, this time through the exchange’s own internal AI tool. On October 29, about $6.34 billion left Binance’s wallets.
In 2026 alone, the same team caught and stopped 57 threats it linked to North Korea. The figure comes from the incident report the exchange published on November 3, 2026. This one got through. An earlier article covered how the money was moved. Now the report shows how the attackers spent five months working their way to the wallets: through a search engine, a job interview at a company that does not exist, and an AI tool built for employees.
A trap in the search bar
The engineer worked on the Wallet DevOps team, the people who run the servers behind the exchange’s wallets. The report calls him Engineer A and does not name the AI assistant he was after.
Homebrew is a free package manager for macOS, a kind of app store for developers: type one command in the terminal and the program you need is installed. Compromise the store itself, and everything installed through it passes through the attacker’s hands.
The Homebrew trick is not new. In January 2025, developer Ryan Chenkie spotted a Google ad that displayed the real address, brew.sh, but led to a fake one, brewe.sh. The site told visitors to paste an install command into the terminal. The command launched Atomic, a spyware program that steals passwords, browser data and crypto wallets. Binance does not say which page caught its engineer.
The security team moved fast: new computer, new passwords, new access keys. It looked like a happy ending. Almost. By then the attackers had learned what Engineer A did and who his colleagues were on the team responsible for the exchange’s wallets. All they needed now was an excuse to start a conversation with one of them.
Interviewing with the CEO of a ghost company
In September, another employee, Engineer B, got a message on a mainstream job-hunting platform. His profile listed his work at Binance. The sender introduced himself as a project director at a company that, it later turned out, did not exist.
From there it looked like ordinary hiring. A “human resources” contact ran the first round: a live video call, plus a social media account full of personal photos and videos to build trust. The “CEO” led the second round, this time over a popular chat app. At the end, he asked Engineer B to download a coding assignment, a repository of code. Engineer B put it on his work computer.
The trap sprang during setup. A script swapped out pyenv, a small utility that switches between versions of the Python programming language. It deleted the real one, installed a copy of its own and pointed the link at the copy. From the outside, nothing changed. Inside, the fake took orders from the attackers’ server. The company’s endpoint protection, the security software on every work machine, never noticed, and the script cleaned up after itself.
Binance calls the program “0-day malware.” Vulnerability analyst Will Dormann replied on Mastodon with a flat “No” (as quoted by Help Net Security). No one broke in through a hole in any software. A person ran a new program that the antivirus had simply never seen.
An AI tool as a skeleton key
Two infected computers still do not open the wallets. On October 20, the attackers took the next step. Working from Engineer B’s computer through an internal AI tool, they took over the machines of two wallet developers: Engineer C and the same Engineer A whose computer had been replaced in June. The report does not say how the AI tool was abused, only that Binance has since rebuilt it from scratch, access controls included.
On Engineer A’s machine, the attackers found a pass that let them launch their own programs on the exchange’s servers in an employee’s name. Technically, it was a container deployment token.
On October 29, from 17:15 to 19:56 UTC, the attacker worked from Engineer C’s computer. He logged in with Engineer A’s credentials and launched his own program on an exchange server. That got him into the signing service, the system that puts a digital signature on every transfer out of the exchange’s wallets. At 20:05, five hot wallets, the kind kept permanently online, began sending XRP to an outside address. In four minutes, 233.46 million coins were gone. Three more cryptocurrencies followed. Binance puts the total loss at about $6.34 billion.
Halting withdrawals was not enough. The attacker had planted his own proxy program in one of the exchange’s hot Ethereum wallets, and it kept working even after Binance shut withdrawals down. That earlier article covers it in detail. Because the wallet’s key is split among several parties, no single signature could revoke the proxy, and the exchange had to devise a separate procedure. The last transfer through the proxy, 2,961.9 ETH, went out at 23:56 UTC. Binance revoked it at 00:10, 14 minutes later.
// Timeline
- Engineer A searches for an AI coding assistant and installs a fake Homebrew. His computer is replaced, but the attackers already know his team.
- A “project director” contacts Engineer B. Two interview rounds, then a coding assignment on his work computer.
- Through an internal AI tool, the attackers take over the machines of Engineers A and C.
- Login from Engineer C’s computer, the attacker’s program launched on a server, the signing service reached.
- Five hot wallets send 233.46 million XRP to the attacker’s address.
- The exchange revokes the attacker’s proxy program in its hot Ethereum wallet.
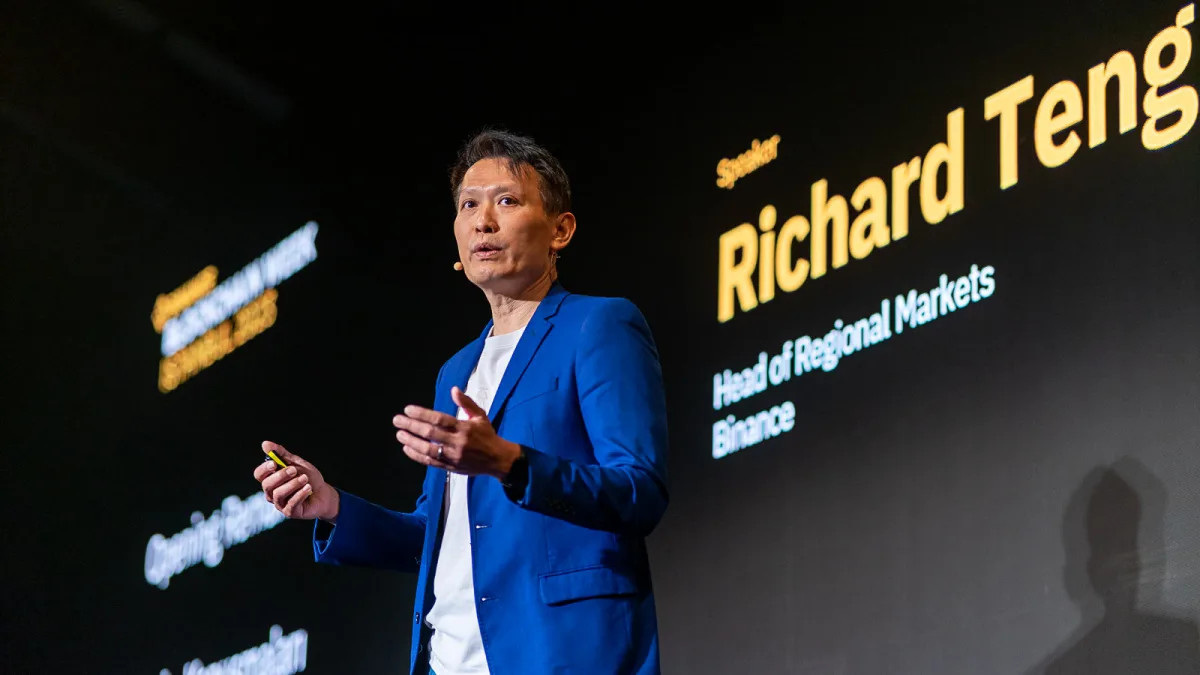
The attackers “spent months building their way in,” Richard Teng, one of Binance’s two co-CEOs, told CNBC. He dismissed the idea that one employee’s laptop decided everything, and the report, too, describes a multi-stage campaign. The FBI attributed the theft to the North Korean group TraderTraitor, the same group that stole $1.5 billion from the Bybit exchange in February 2025. Pyongyang called the U.S. claims “preposterous nonsense.”
Binance has covered its customers’ losses from its own reserves. By October 31, the report says, it had replenished 98% of the stolen assets, and about $2.85 billion of the stolen money has been frozen or intercepted.
An interview thousands have sat through
Binance does not link its case to any specific campaign. But the script is a familiar one: a recruiter, two rounds, a coding test. In September 2026, police and security agencies in Japan, the United States, Australia and Germany issued a joint advisory about a North Korean group called WaterPlum. Its campaign is known as Contagious Interview.
Between December 2025 and July 2026, WaterPlum infected at least 30,000 devices in more than 100 countries. It reached the funds or credentials of more than 7,000 crypto wallets and sent about 1.7 billion yen, roughly $10.7 million, back to North Korea. That works out to about $350 per infected computer. Each victim is small change. There are simply thousands of them.
WaterPlum’s main targets are ordinary job seekers. The scammers pose as AI, crypto and NFT companies and reach out through recruiting and freelance platforms. During the interview they ask candidates to download a project, “fix” a video-call glitch or run some code. The malware then grabs, among other things, browser passwords and crypto wallet keys.
You do not need to know how to code to fall for a request to “fix the video call.” You only need to be looking for a remote job in a hot industry. A call like that can cost a job seeker their personal wallet. Take it on a work laptop, and the employer is exposed too.
The scheme also runs in reverse. According to the agencies, some WaterPlum members land remote IT jobs themselves, using documents stolen from victims. In interviews, they swapped their faces using AI, then switched off the camera and blamed a bad connection.
The coding test you should not run
It has long been said that the cost of hiring a new employee is “significantly higher than paying to retain an existing employee,” Tyler Reguly of the cybersecurity company Fortra noted. For Binance, he added, “that cost was astronomically higher.” With quiet quitting widespread and plenty of people doing the bare minimum at work, employees interviewing on company time should surprise no one, he said. So companies need to control what can be downloaded and run on work laptops, and what permissions users have on them.
The agencies have two pieces of advice for job seekers: run unfamiliar code only in an isolated environment, known as a sandbox, and check the files beforehand for commands that pull anything else from the internet. The other warning signs come straight from the stories above.
Binance co-founder Changpeng Zhao wrote on X that “some details are embarrassing.” “No platform is unhackable, but that cannot be an excuse,” he added. The attack, he said, ran for months and targeted hundreds of employees and systems, with only a few compromised. The report shows which ones. Engineer B downloaded and ran a coding test from a company that does not exist right on his Binance work computer. And the way in, once again, ran through Engineer A, whose computer and passwords Binance’s security team had already replaced in June.